
I. INTRODUCTION
The inefficiency of existing implementations of RSA cryptosystem in real-time applications calls for identifying new methods that would allow to take advantage of its otherwise attractive features. Currently there are no known methods analogous to RSA algorithms that could protect information in real-time applications such as mobile or voice communications. We consider the possibility of using a modified RSA algorithm, labeled RSA-m. The idea underlying the modification is to send not the encrypted information through open or even secured channels but only some specific data about its encryption instead. We offer several versions of such a modification which, however, require additional research. The ultimate purpose is to increase the working speed of the algorithm similar to RSA system to exploit its full potential in real-time information transmission.
The relatively low working speed but high cryptographic resistance of the RSA system motivate the cryptographers' search for potential improvements to the system to enable its use with the typical information flows or for securing of real-time information where privacy needs to be protected in the short term (from few minutes to several months). Below we consider one of such procedures, based on transmitting not the information itself, but only some indirect data about this information in real time. The amount of these data is much lower than the original information and, therefore, these data can be transmitted in encrypted form with required crypto resistance through the channels with limited speed and bandwidth (e.g., 64 KB/s) based on the use of, e.g., RSA cryptosystem, but without significant delays in time. The amount of transmitted information can be significantly reduced, e.g., by representing it in the formant form, which allows to reduce its encryption (decryption) time to be commensurate with the bandwidth of mobile communication channels. Another strategy for modifying encryption algorithms in mobile communications in this case is based on the use of short keys, but with the provision of the high speed of their turnover. The author considers this extension in another publication.
II. INFORMATION PROTECTION USING RSA-MAB ALGORITHM
The main idea of the proposed algorithm is in using so-called numeric formants, which were introduced in [1] and detailed in [2] and [3]. Numeric formants allow to represent any number as a simple linear structure. Moreover, the time needed to represent and to recover the number for the encryption and decryption will be significantly lower than the time required when using of the algorithms of the classical RSA system.
It is known from , that linear and/or nonlinear formants using only 3 or a few more parameters, allow to significantly reduce the length of the digital message regardless of the length of the transmitted number n. The advantage of such an approach is that the so-called base of the formant can be any simple or composite number of substantially lower length than is required for the encryption in the classic RSA cryptosystem.
Below we consider several algorithms using linear formants for the transmission of the information requiring short-term secrecy, where the amount of time needed for encryption and decryption is considerably reduced, even after accounting for the additional operations for transforming the message.
a) AB1 Algorithm
As known from [2] and [3], any number can be represented, in terms of the formant analysis, as a binomial structure , where is the formant's base, is the core and is the remainder. Knowing these three arguments allows us to easily recover the initial number. Types, properties and characteristics of the formant algebra are described in [1].
This way of representing numbers allows to encrypt not the number N itself, but only 3 small numbers instead. The main difference is that N is a large number of the order of or higher, while p, k and q are any whole numbers, simple or composite, the length of which is determined only by the required transmission speed through an open channel. It is recommended to choose the base of the formant p as a number with a length of the order of magnitude of the RSA key, such as a number, corresponding to the block cipher and which doesn't lead to the reduction of the transmission speed. This recommendation allows to use the RSA keys of the medium length, while the presence of the fast simple number generator in the system allows to change them quickly, even in the block format, which will obviously increase the difficulty of hacking.
To implement the RSA-m algorithm, a dynamic database is created in the memory, for instance, in a format of the matrix P with indexed cells which keep pre-generated information used for the formant construction. For example, a matrix can contain such information for 10,000 different formants.
After each single use of all of the values of the matrix P the algorithm prescribes an automatic update of all cells of the matrix, on sending and receiving sides.
Depending on the required strength of the encryption, the matrix in the memory of the microprocessor may be built with a hard or flexible updating program, with an automatic or manual transmission of the matrix. In one version it could even be the same matrix, where the cell names are changed based on an index. The remainder and the core values are then encrypted using the RSA-m algorithm, cryptoresistance of which is guaranteed by the switch in real-time of the keys for each binomial d-bit number of an analog signal or of a symbol (number, byte, block) in an open digital message. On the receiving end, the message is decrypted with a special procedure, which recognizes transmitted cell addresses and decrypts other arguments of each formant, allowing to restore the true value of the transmitted numerical message. The message itself can be a text message in any possible language, an image of any class and type, a piece of speech or music, etc. Figure 1 contains a block-scheme of the AB1 algorithm.
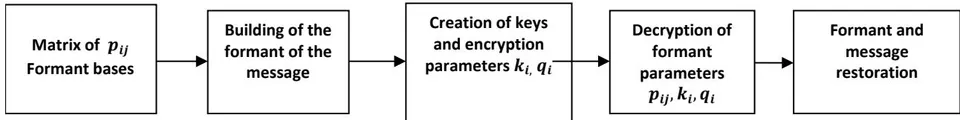
From the analog signal being transmitted, after digitizing it, the block is formed: binomial message of 32(64)... bit;
From the basic matrix block in the memory of the device the base of the formant is randomly chosen and recorded in the cell d1;
Numeric block 64 bit (Ex. 1) is represented in the formant format. Its core k and remainder q are defined: and ;
The encryption keys for encrypting numbers and are chosen;
5. The message d1d2d3 about the formant is formed;
6. The message d1d2d3 about the formant is encrypted;
7. Encrypted data is passed through an open channel;
8. The block of 64...bit is received;
9. The base of the formant is extracted from the received block;
10. Numbers and are extracted from the block;
- The message-formant is recovered: .
Let's consider a simple example that illustrates the RSA-m algorithm's application.
Example 1. Let's encrypt the message "HFTY". For simplicity we will use small numbers (in practice, much larger numbers are used, by several orders of magnitude).
Let's pick two simple numbers and . Their product is .
Find . Therefore, the number for the private key d can be chosen to be smaller than 20 and a co-prime integer with 20, e.g., d=3 (or another: 7, 11, 13, 17, 19,...).
Now let's select an open key - number . We can choose any number that satisfies the relation . With , must satisfy as e.g., does. Indeed, ; .
Let's represent the message that is being encrypted as a sequence of whole numbers by applying, e.g., the following assignment: , , , . Then the encoded message is then: " . Let's encrypt this message using an open key .
Cipher ; first we raise the number to the power, then divide it by modulo N. The division remainder yields the result of the encryption.
Thus, the open message can be represented as an encrypted message SE1, i.e., the numerical sequence , which, for instance, corresponds to the text "PFLJ".
- Now let's create an encrypted message for the transmission through an open channel that includes the auxiliary information, for example, of the following type (it can be of any order or content).
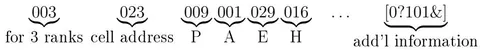
The first three decimals - the digit number for the code processing; shows us the length of the machine word, i.e. every three decimal digits.
The second group of decimals - the cell number of matrix P in memory, which the controller on the receiving side must extract from memory.
The third group of three decimal digits contains information for the decryption with RSA algorithm (can contain any number of the "triples" depending on the length of the sent block of bits - 16, 32, 64 etc.).
The last, for instance, 6 or more digits include additional service information: the ending of the sent message, the parity check etc. Thus, while sending 64...-bit, we must choose the first and the last 6 digits, which contain all the information about decryption of the remaining 58 decimal digits.
We created encrypted message , which is the result of the cryptography with a secret key . On the receiving side in the cell the corresponding numbers are located: "private key d" and the modulus of the cryptokey: d=3; N=33. That is why it is so easy to decrypt the encrypted message "912916".
Let's decrypt the received encrypted message on the basis of the private key . We get
Initial T1 =
Initial T2 =
b) AB2 Algorithm
Version 1. Storage cells indexing.
In the matrix of 10,000 cells (1000 rows x 1000 columns) the cells are numbered in the natural order; they can also be represented as a double-index variable , where . For example, the cell #457 has index , and the cell #4057 will have the number or index-address .
Each cell of the matrix P, will now contain the index number, which is encrypted by RSA-m system. For instance, in the cell #0009 this number is 3; cell #0001 will contain number 1; cell #0029 - number 2; cell #0016 - number 4, which corresponds to the decryption with the key d = 3; N = 33; and encrypted with the key e = 7. Other cells of the array will be filled in exactly same way.
The algorithm of the cell mixing in Version 1 does not change the cell's content; it only changes it's index number.
To further increase the cryptoresistance level of the RSA-mAB algorithm, we could randomly change the length of the encrypted blocks, with the corresponding change of the cryptokeys' length. The number of such arrays and their size depend on how long the information needs to be kept secret and on the memory size of the controller on which the RSA-mAB will be realized.
Version 2. Application of the formant analysis. The block-message with the length 32 (64)...bit is formed.
The formant base is randomly selected from the basic matrix and its number is written as the message (the base of the created formant is stored in the cell ).
The initial number of the formed informational block is represented in the formant form, and all its remaining parameters (the core and remainder , are defined by the selected base and are written in the messages d2 and d3.
3. Transmitted message d1d2d3 is formed.
Crypto keys for encryption of cores and remainders are generated.
The message about the formant is encrypted.
Encrypted message is transmitted through an open communication channel.
The block 64... bit is received.
Coordinate-address is extracted from the received block.
The value of the formant base is restored.
and are extracted from the corresponding block.
The formant is restored from the encrypted message using the standard formula.
As a similar example, consider the encryption of the message "EDA" or of its numeric code 651. Let's represent the 651 code in the formant form, i.e. as the sum of a product and a remainder, and choose as the base, e.g., random simple numbers 237, 54, 119, etc. The matrix of the RSA-m system keys from Version 1 is replaced by the format's base matrix, which creates the first set of the randomly chosen bases of various length and properties (simple or composite). Returning to our example, recall that our message is: S2 = 651.
We choose the base randomly, e.g., . In the controller's storage write down .
Calculate the formant of the number 651 on the base 54: . Write down in the storage it's arguments: and .
The machine defines the length of the information block S0 being formed for encrypting (for example, the first three triples of decimals): S0 = 054012003.
Choose the encryption key from the cell #54 of the key matrix in memory.
The message is encrypted:
Thus, the encrypted message will take the following form: 012012028. Next, we form the transmitting block with the additional service information and send it through the open channel to be decrypted on the receiving side:
Decrypt the block, which yields
Restore the formant: .
III. CONCLUSION
The discussion and the examples provided above illustrate the conceptual possibility of transmitting encrypted voice messages in real-time mode with transmission speed of about 64 kb/s, using, for example, the connection channel such as Telegram or Telegram Messenger.
Clearly, other approaches based on the use of formants for message transmission are also possible, e.g., 10 different approaches are described in [3]. We considered the most obvious ones. For example, matrix contains decimals (digits), which will be encrypted with 64 different keys. First, 64 bit digits are encrypted (rank: 6 decimal digits). Double the number of digits and begin encrypting 124-bit numbers in order to raise the rank to 12 decimal digits. bit-numbers and each 10-bit number is located in the cell of matrix .
For matrix matrix with a rank of 10 decimals (number of bits) – there are of digits selected, which are encrypted with the key K1. In matrix M2 the same 4,096 digits are selected, but encrypted with another key K2, etc. Then, matrices MZ - K Z, where Z represents the length (number of bits) of encryption keys, for example 10 or 100 etc. what allows to significantly reduce the duration of encryption by replacing multiple number multiplications with simpler processes. This allows to use the RSA-mAB1 algorithm for protection of real-time information and to improve the stability of cryptographic keys with frequent changes in the block length.
MZ matrices can be built separately (independently) using different methods. In the AB1 algorithm this operation differs with respect to the content of the matrices, because they were created with the use of different keys.
AB2 algorithm uses one and the same matrix, with unchanged content of its cells, but it changes cell addresses. The redistribution of cells' contents of matrix M can be implemented in various ways. It can be random or according to some algorithm applied to each matrix cell such as, e.g., the relation , changing k and j in a such way, that all or just some cells are affected by the algorithm.
Our library of algorithms includes an extended algorithm which allows to use any of the algorithms described above for real-time crypto-problems. Obviously, such message will be more difficult to decrypt in a relevantly short time. Even with writing a message on hard media, it can not be reasonably quickly decrypted so that hacking will require dozens of years, as the hacker knows neither the length (range) of keys, nor the block length, nor the transition rule from one pair of keys to another. Besides, he doesn't know the keys at all.
This is internal information of the security system. Each external communication can of the same type, but its content will differ in the meaning of the information transmitted in each session and the same phonemes will be represented in different messages by different codes.